

Audit-Ready Architecture
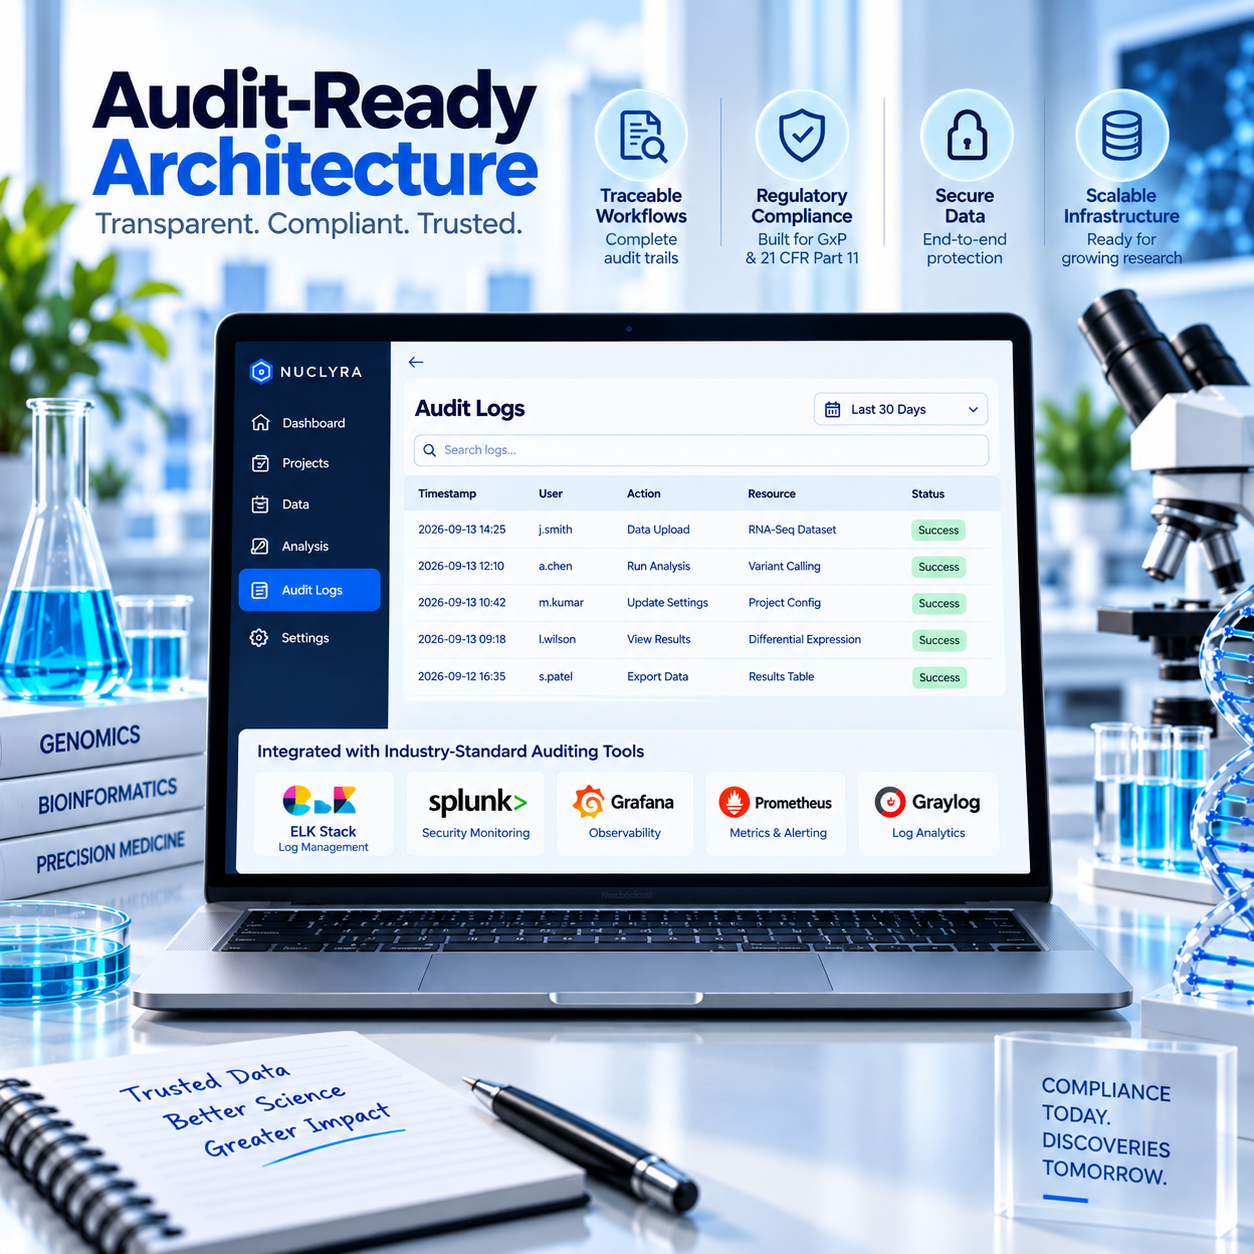
Application architecture built with the access logs, version history and change control that a real audit requires — designed in from the first commit, not bolted on after the fact.
TYPICAL CLIENT
A compliance or engineering lead whose software has to survive an audit, not just a demo
Usually a Compliance Lead, Head of Engineering or QA owner at a diagnostics, pharma or health-data company whose application itself — not just the model behind it — needs to hold up under regulatory or security review.
Six concrete deliverables, not a slide deck.
This is exactly what transfers to you at the end of this engagement.
Architecture documentation & data flow diagrams
A clear record of how data moves through the system and where every access point sits.
Access-controlled, versioned application
An application built with role-based access and version history from the start.
Audit logging for every data access & change
A complete, queryable log of who accessed or changed what, and when.
Change-control & deployment record
A traceable record of every deployment and configuration change, ready for review.
Security review / audit-readiness report
An honest written assessment of where the system stands against your audit requirements.
Source code & infrastructure-as-code
Full repository access plus infrastructure configs, transferred outright.
What this service includes
Architecture design for auditability
Systems designed so traceability is a byproduct of how they run, not a document written after the fact.
Access control & authentication
Role-based permissions and authentication built to match your organization’s actual access policy.
Audit logging & change tracking
Every data access and system change logged automatically and kept queryable for review.
Security review & compliance documentation
A structured review against the standard your audit or due-diligence process actually requires.
What this looks like in a real engagement
Three concrete examples of the kind of work this service covers.
Rebuilding a clinical data portal for a security audit
An existing portal re-architected with proper access control and logging ahead of a scheduled security review.
Adding full audit logging to an existing LIMS
Audit logging retrofitted onto a system that had none, without a full application rebuild.
Access-control redesign ahead of partner due diligence
A redesigned permissions model completed before a partnership’s technical due-diligence review.
Why audit logging bolted on after the fact is never quite enough.
Adding logging to an existing system after an auditor asks for it usually means gaps: the access that happened before logging was added, the change nobody thought to record, the log that exists but nobody can actually query under time pressure.
We design the architecture so every access and change is logged as a natural byproduct of how the system runs, so when the audit request comes in, the record already exists.
How an engagement runs
Four stages, from initial scope to delivery.
Map audit requirements
We identify the specific access, logging and change-control requirements your review process expects.
Design the architecture
Access control and logging are designed into the architecture itself, not planned as a later addition.
Build with logging built in
The application is built so every relevant access and change is captured automatically.
Review & document
A readiness review and documentation are prepared ahead of the actual audit or due-diligence process.
What we build it with
The audit took two days instead of two weeks, because the logs already existed.
Before you reach out
Yes, though coverage will depend on what the current architecture already captures; we’ll tell you honestly where gaps remain after a review.
Access control, logging coverage, change-control records and data flow — assessed against the specific standard your review process requires.
Yes. Architecture diagrams, access-control documentation and the audit-readiness report are written to be handed to a reviewer directly.
Explore related work
MLOps for Regulated Environments
The equivalent audit-ready approach applied to deployed ML pipelines.
View APIAPI & Integration Development
Building the same integration layers with full audit logging in place.
View WEBScientific Web Applications overview
See how audit-ready architecture fits into the full service.
ViewPreparing for a security or compliance audit?
Tell us what the review process expects to see — we’ll tell you honestly how ready your current architecture actually is.