

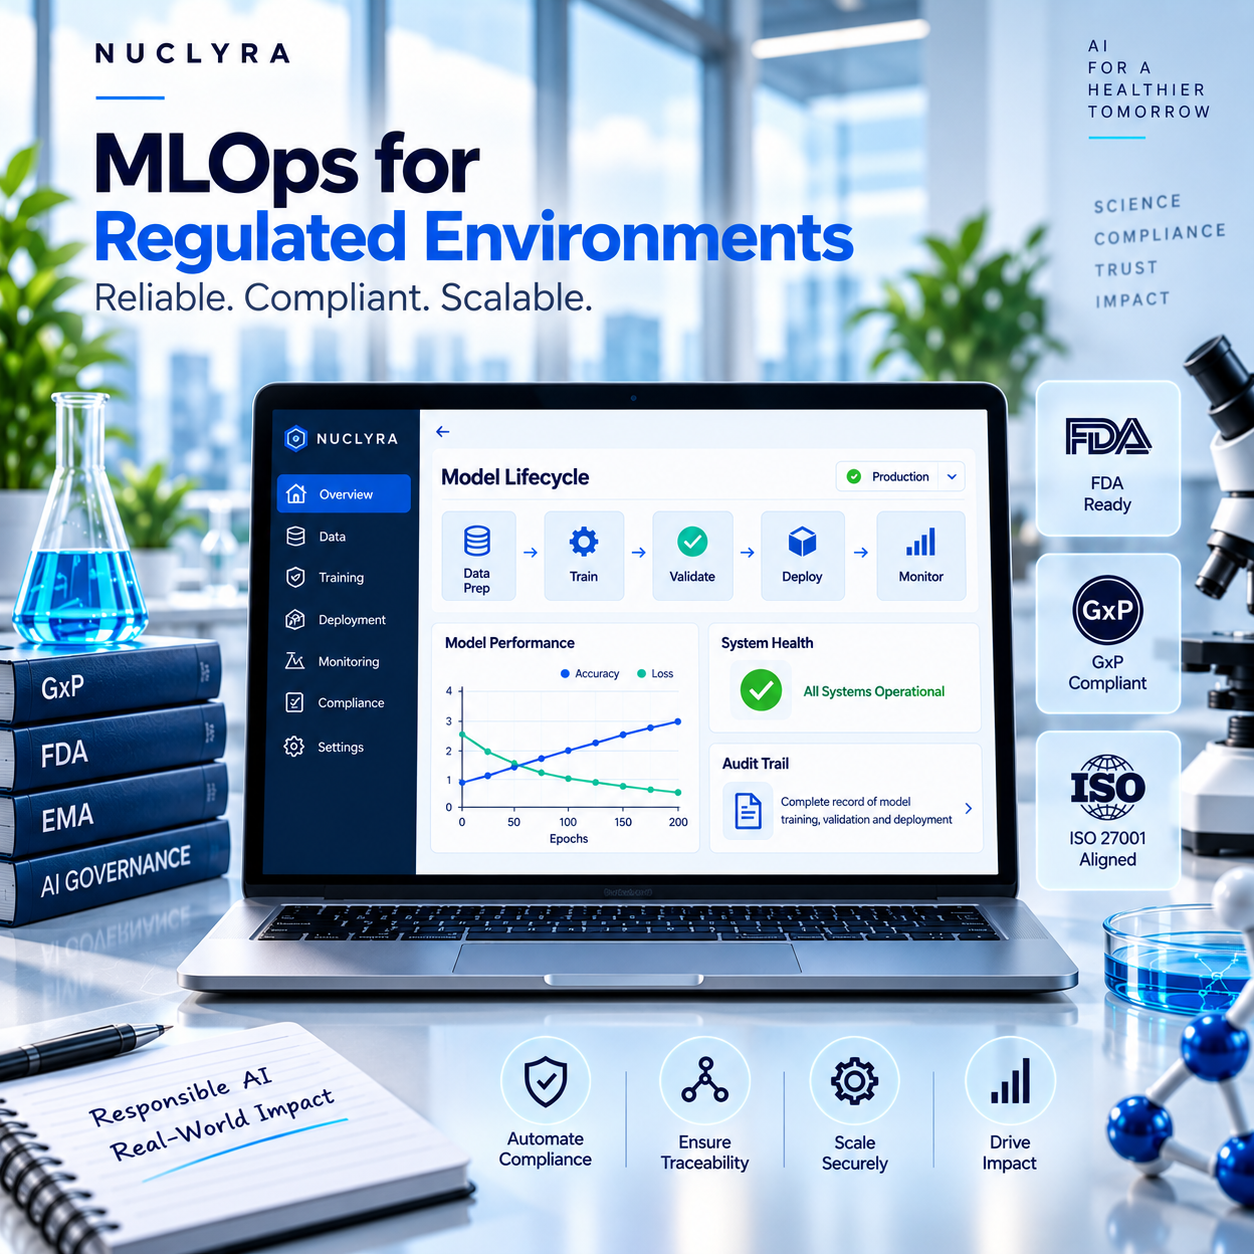
MLOps for Regulated Environments
Deployment, versioning and monitoring infrastructure built for audit trails and change control — not a CI/CD pipeline borrowed from consumer software.
TYPICAL CLIENT
A platform or engineering lead deploying models under regulatory scrutiny
Usually a Head of Engineering, Platform Lead or QA/compliance owner at a pharma, diagnostics or health-data company who needs models deployed with full audit trails, access controls and validation records that will hold up under review.
Six concrete deliverables, not a slide deck.
This is exactly what transfers to you at the end of this engagement.
Versioned model & data lineage tracking
Every model, dataset and training run tracked and traceable back to its exact inputs.
Automated validation & retraining pipeline
Retraining triggered on a schedule or by drift, with validation gates before anything reaches production.
Access-controlled deployment environment
Role-based access to models, data and deployment actions, matched to your existing identity system.
Drift & performance monitoring dashboard
A live view of data drift and prediction performance, with alerting before quality quietly degrades.
Audit trail & change-control documentation
A record of every model version, deployment and configuration change, ready for review.
Full source code & infrastructure-as-code
The complete pipeline and infrastructure definitions transfer to you, not just the running system.
What this service includes
Model & data versioning
Every training run, dataset snapshot and model artifact tracked and reproducible on demand.
Deployment governance & access control
Role-based permissions and sign-off gates built into the deployment path itself.
Drift detection & monitoring
Automated alerts when incoming data or predictions start to diverge from what the model was trained on.
Audit trail & compliance documentation
A complete, exportable record of what changed, when, and who approved it.
What this looks like in a real engagement
Three concrete examples of the kind of work this service covers.
Deployment pipeline with a full audit trail for review
A regulated diagnostics model deployed with every version, dataset and configuration change logged and exportable for auditors.
Drift-triggered retraining with sign-off gates
Automated retraining kicked off by drift alerts, held behind a validation and human sign-off gate before promotion to production.
Role-based access across research and clinical teams
A shared model registry with access controls so research and clinical teams see and can act on only what their role permits.
Why generic MLOps tooling assumes the wrong kind of stakes.
Most MLOps platforms are built for teams that can ship a model update and roll it back quietly if it underperforms. Regulated environments don’t work that way — every version, every retrain and every access grant needs to be traceable and defensible after the fact.
We build the audit trail and change-control process into the pipeline itself, so compliance isn’t a document written after deployment — it’s a byproduct of how the system runs.
How an engagement runs
Four stages, from initial scope to delivery.
Map compliance requirements
We identify the specific audit, sign-off and traceability requirements your environment actually needs to meet.
Build the versioned pipeline
Model, data and configuration versioning is built in from the start, not bolted on later.
Deploy with access control
Deployment ships with role-based permissions and sign-off gates matched to your governance process.
Monitor & maintain the trail
Drift monitoring and audit logging run continuously, keeping the record current as the system evolves.
What we build it with
Auditors rarely ask if the model is accurate. They ask if we can show exactly how it got there.
Before you reach out
Yes — we scope the specific validation and traceability requirements your environment operates under before designing the pipeline.
Retraining runs through the same validation and sign-off gates as the original deployment, so nothing reaches production without a review trail.
Yes. The pipeline and infrastructure-as-code are designed to run inside your own environment, under your existing access controls.
Explore related work
Model Development & Validation
The validated models this pipeline is built to deploy and monitor.
View XAIExplainable AI Systems
Explanation and reporting layers that plug into the same audit-ready pipeline.
View PRODUCTSentinel Audit
Our packaged tool for continuous audit logging and access oversight.
ViewDeploying a model into a regulated environment?
Tell us what the review process expects to see — we’ll tell you honestly what it takes to build a pipeline that can show it.